SBOM vs KBOM for Kubernetes: Comparison
Build-time SBOMs show package composition; KBOMs map live Kubernetes workloads—use both for audits, governance and fast incident triage.
Read moreBlog posts in the Compliance Management category
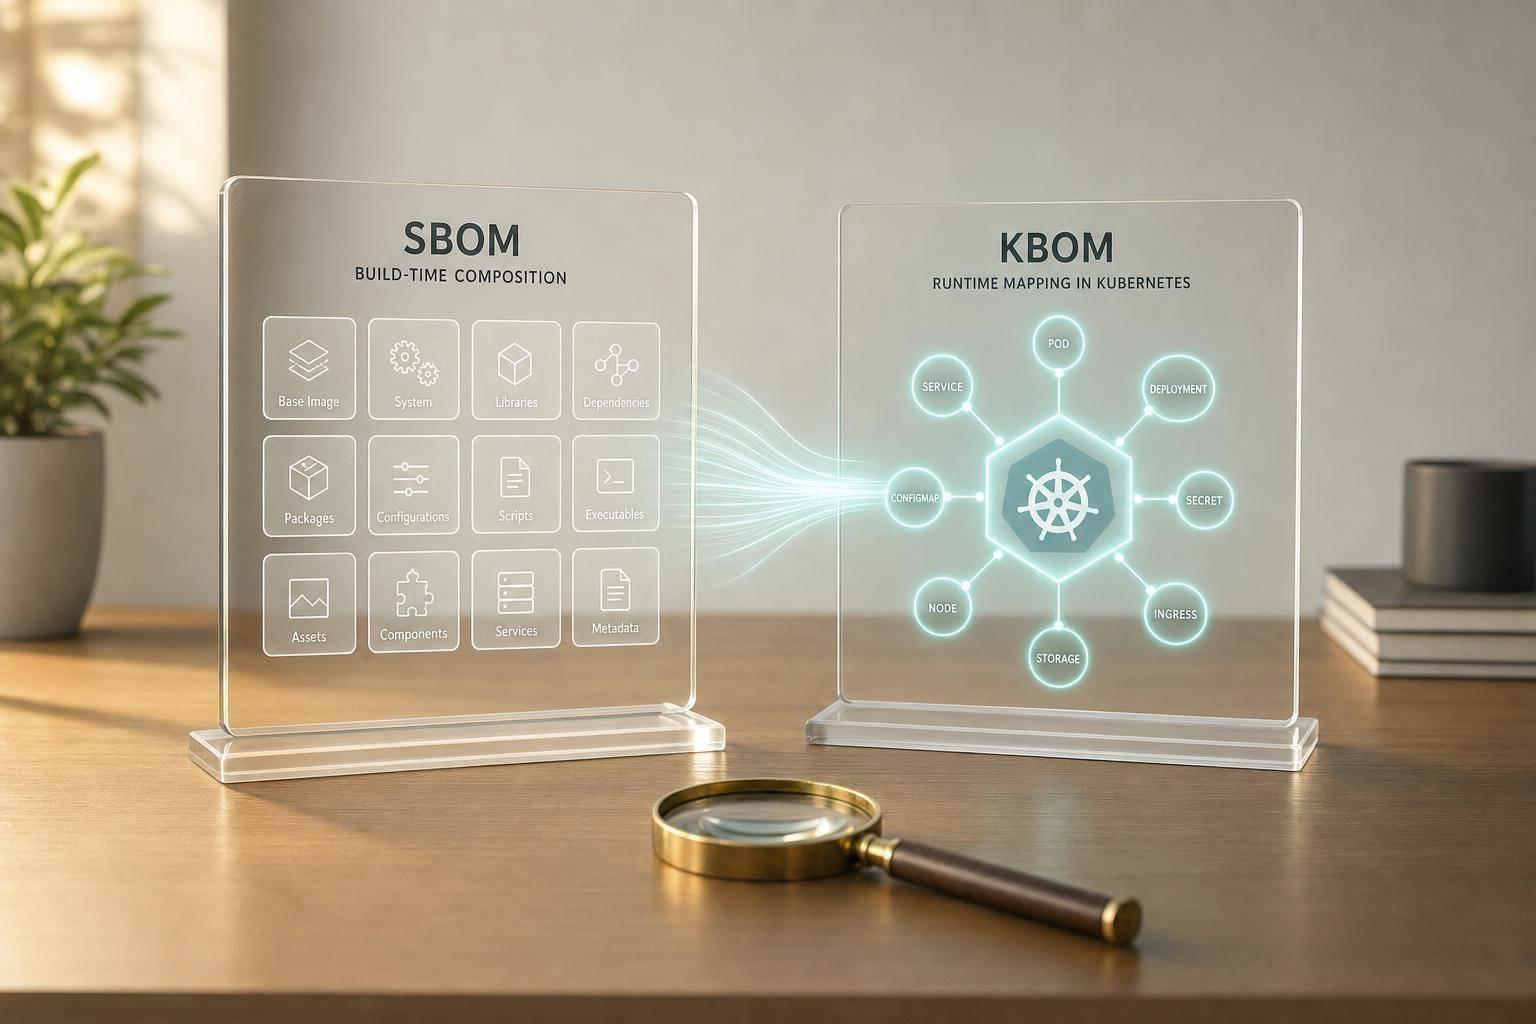
Build-time SBOMs show package composition; KBOMs map live Kubernetes workloads—use both for audits, governance and fast incident triage.
Read more
No single tool secures hybrid cloud — combine policy-as-code, IaC, CSPM, SIEM, evidence automation to prevent, detect and prove compliance.
Read more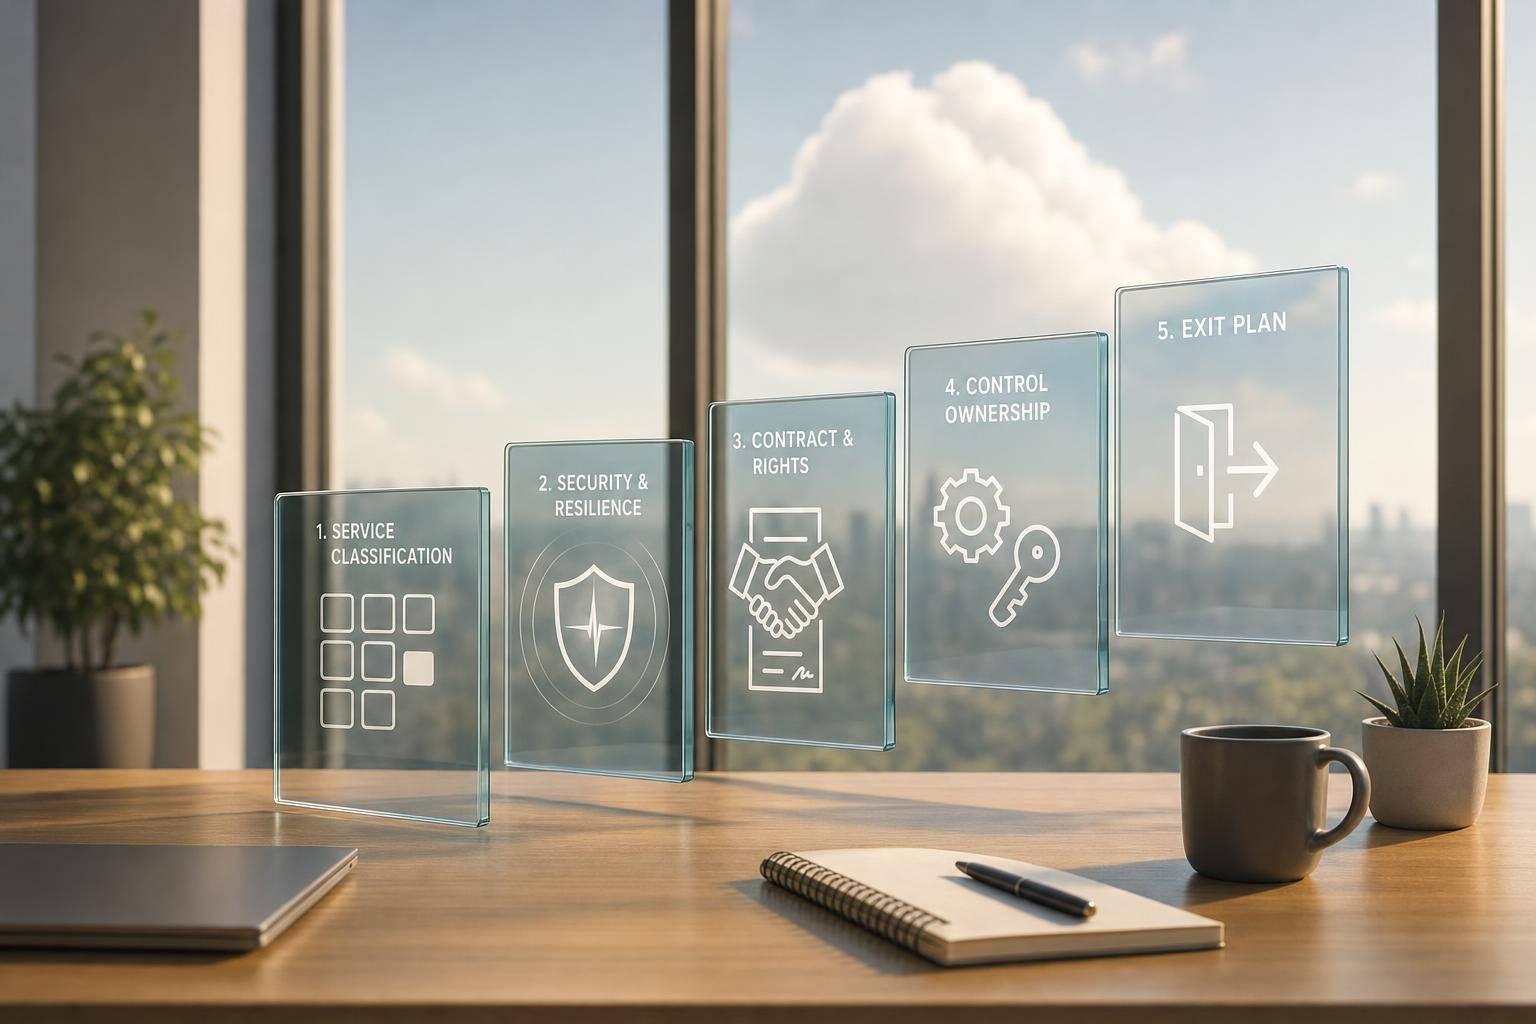
Assess cloud vendors: classify services, verify security and resilience, set contract rights, define control ownership and plan exit.
Read more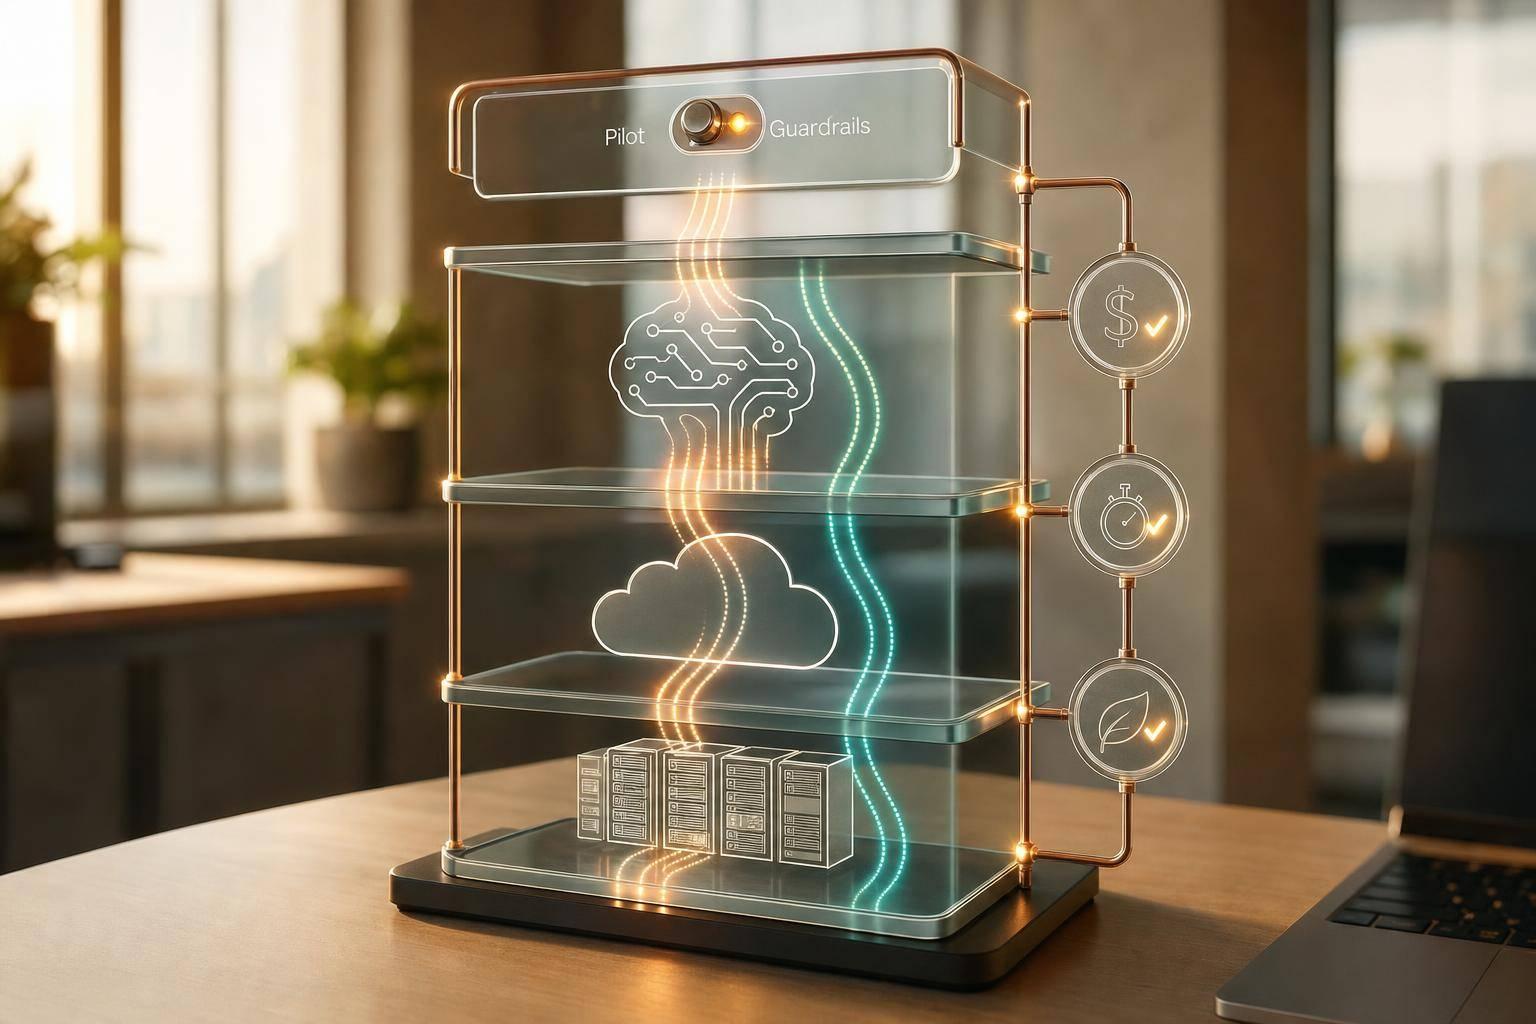
AI-driven schedulers can cut hybrid cloud cost, latency and energy; pilot them with guardrails to manage drift, overhead and compliance risk.
Read more
Use SAML for browser-based enterprise SSO and OIDC for modern web, mobile, SPA and API-driven apps; choose by app type and operational cost.
Read more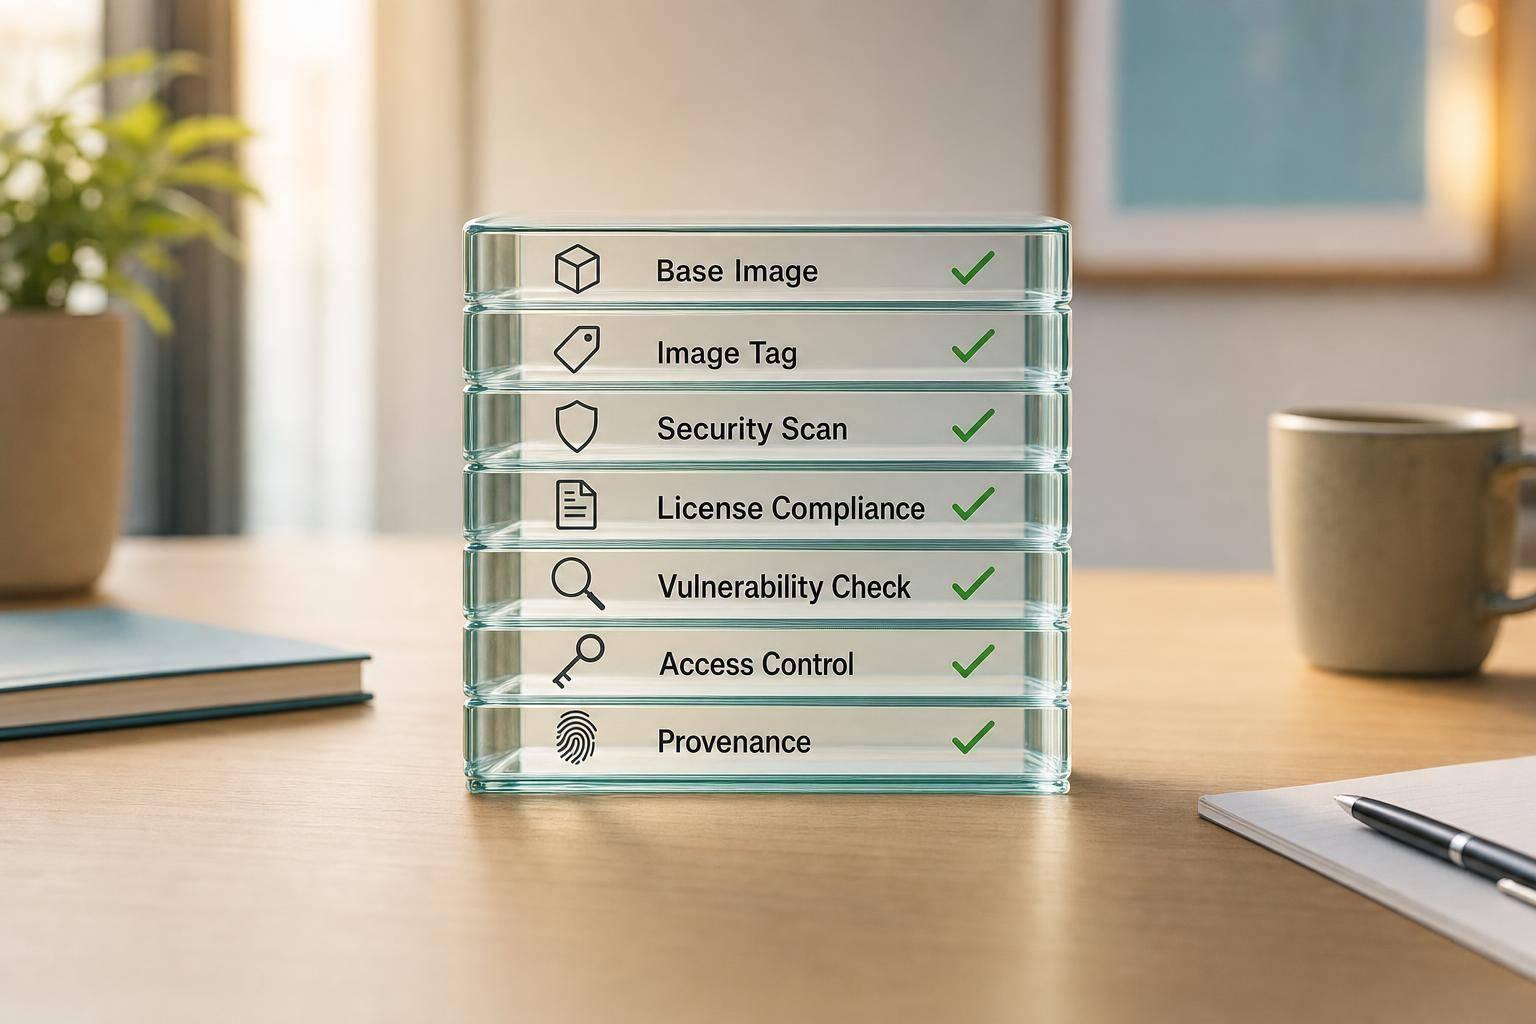
Enforce approved base images, version pinning, signing, SBOMs, non-root runtime, secret/CVE scans and digest-based deployments.
Read more
Compare cloud KMS, HSM and control layers to plan post‑quantum key migration for long‑life data and regulated workloads.
Read more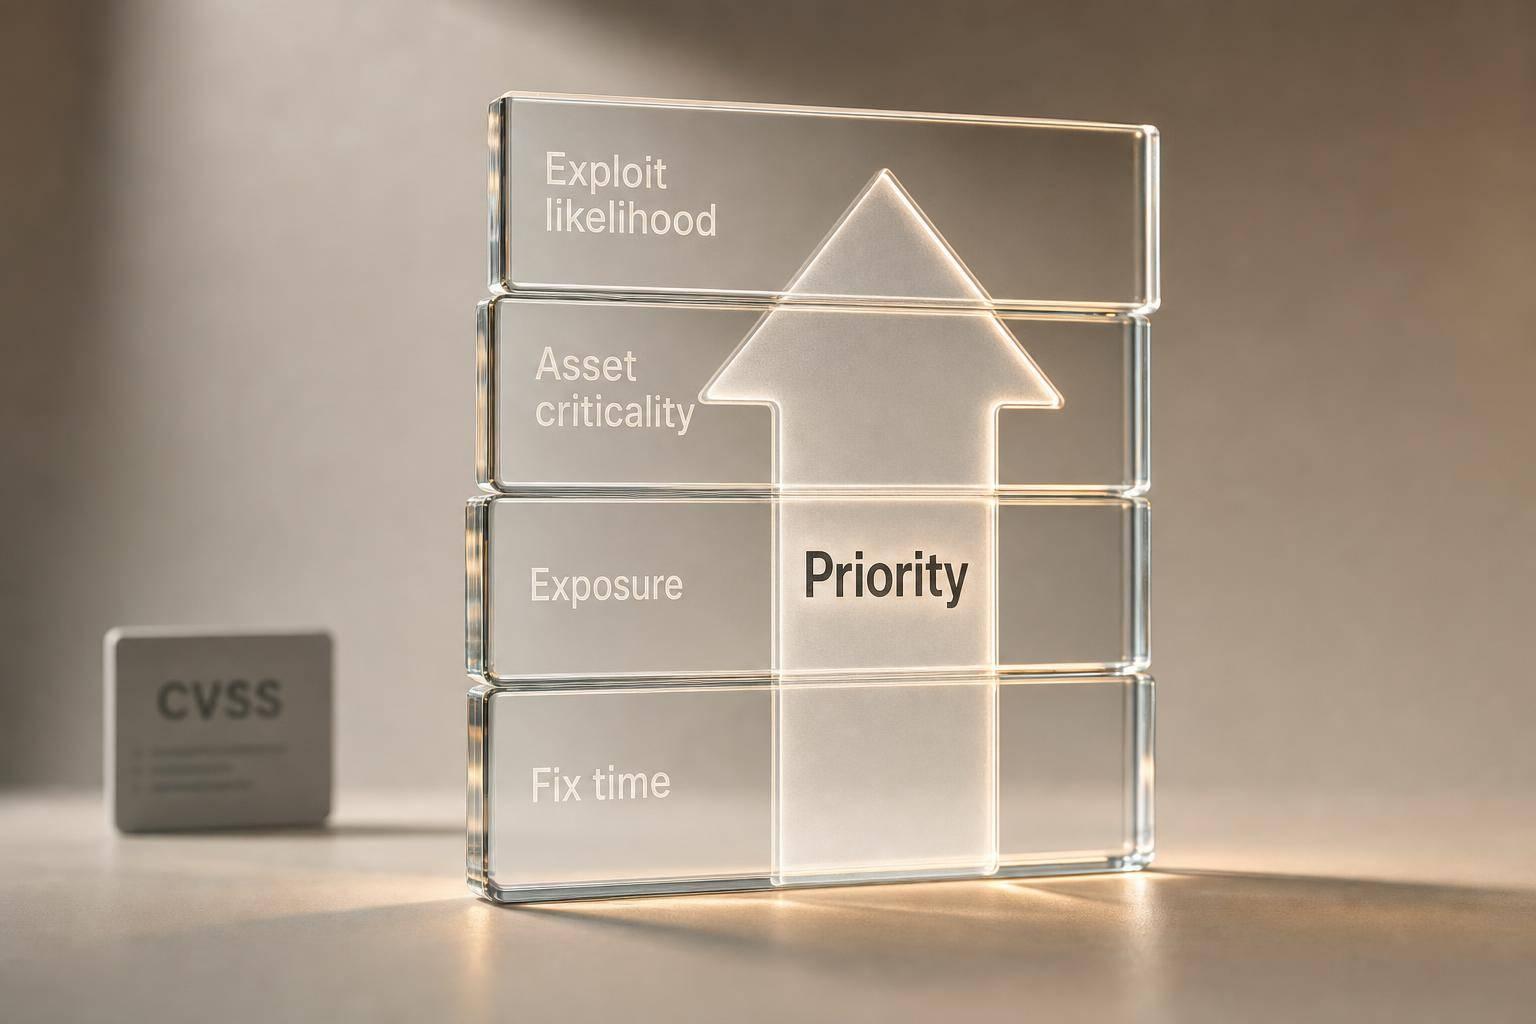
Prioritise fixes by exploit likelihood, asset criticality, exposure and fix time — not CVSS alone.
Read more
AI cuts false alerts and speeds remediation across AWS, Azure and GCP—if controls stay explainable and high‑risk cases keep human review.
Read more
Map identity sources, match each app to SAML/OIDC/OAuth, centralise policies, phase rollouts and test failover for resilient hybrid SSO.
Read more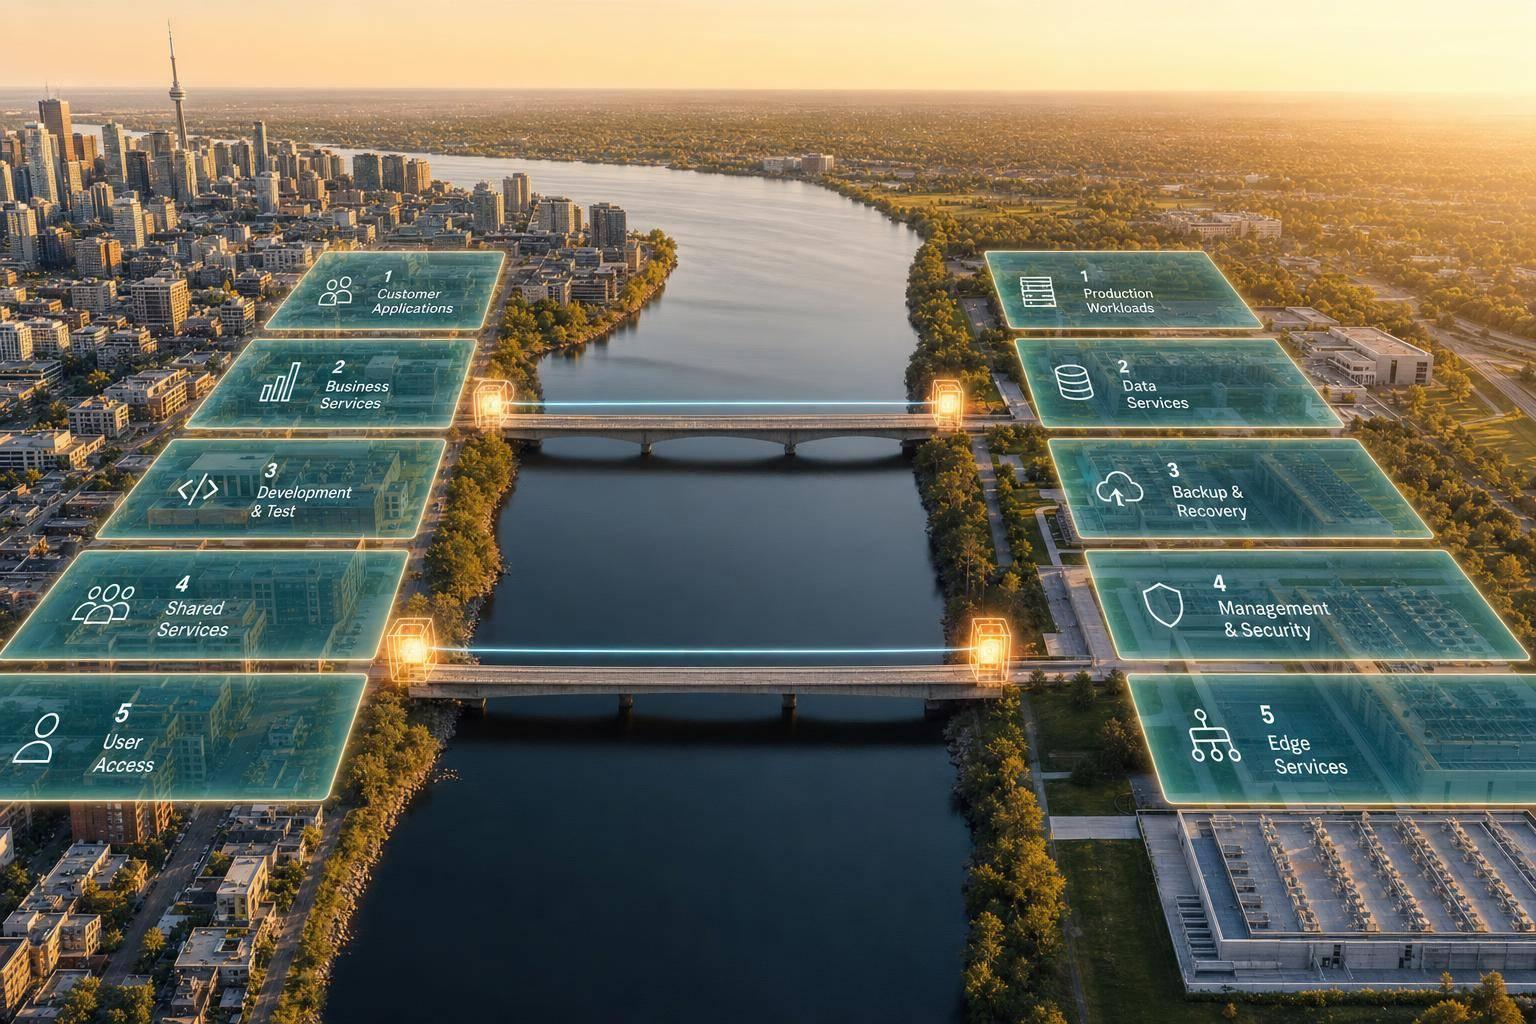
Use hybrid cloud segmentation to separate production, secure regulated data, limit lateral movement and protect app performance.
Read more
Set scope, choose on‑prem tools, automate discovery and CI/CD gates, and enforce remediation SLAs for private‑cloud vulnerability scans.
Read more