Tool Schema Design: 7 Function Calling Practices
Seven rules for designing tool schemas and function calls: clear names, precise types, enums, nested objects and strict runtime validation.
Read moreBlog posts in the Api Security category
Seven rules for designing tool schemas and function calls: clear names, precise types, enums, nested objects and strict runtime validation.
Read more
Treat failed agent tool calls as contract failures: trace versions, isolate mismatches and enforce contract tests.
Read more
Test rate limits, detection and user impact to measure, tune and retest defences against distributed AI model extraction.
Read more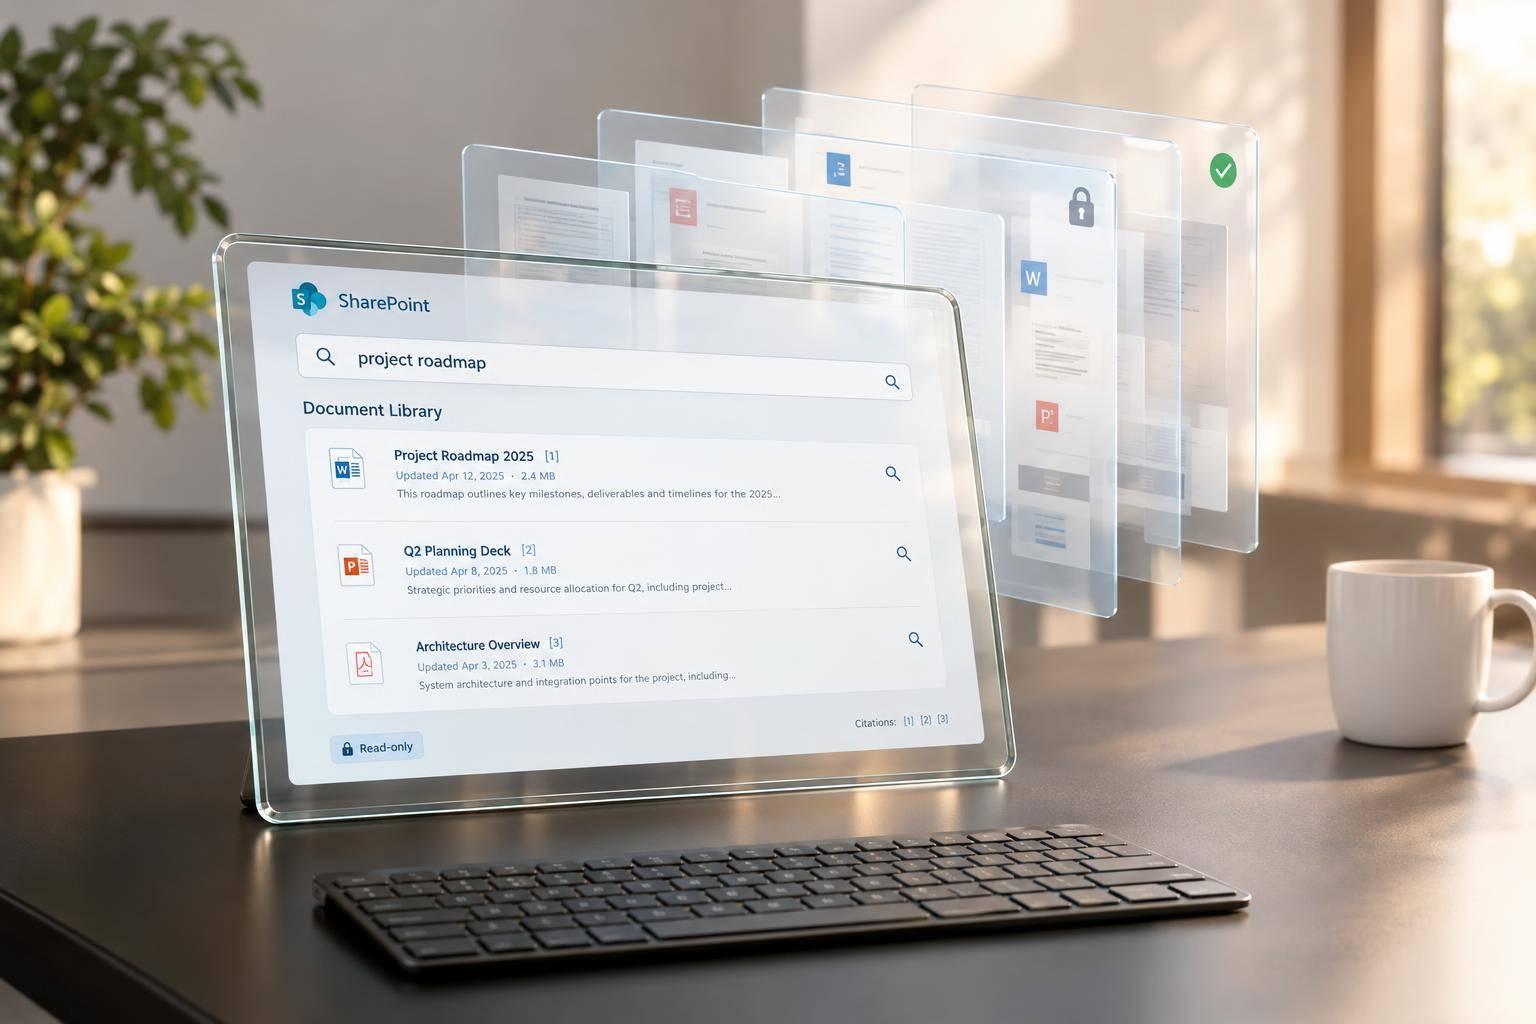
Deploy a read-only SharePoint connector for AI agents with access checks, minimal Graph permissions, cited retrieval and testing.
Read more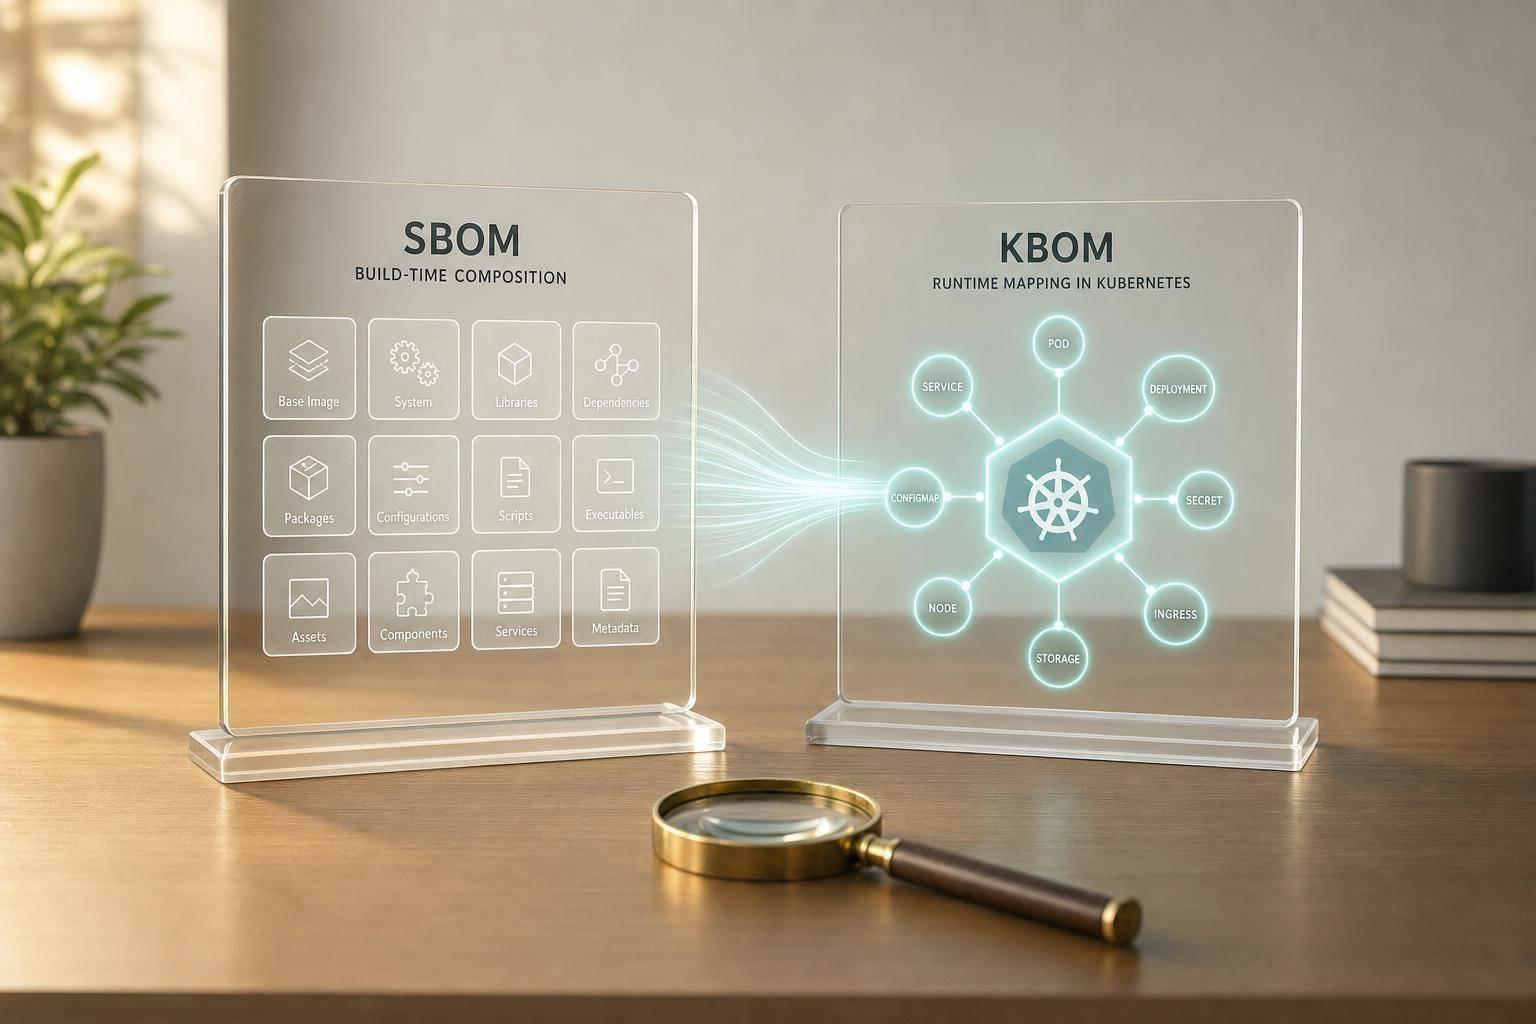
Build-time SBOMs show package composition; KBOMs map live Kubernetes workloads—use both for audits, governance and fast incident triage.
Read more
Use SAML for browser-based enterprise SSO and OIDC for modern web, mobile, SPA and API-driven apps; choose by app type and operational cost.
Read more
Short-lived JWTs, strict signature/iss/aud/exp/scope checks, correct OAuth2 flows (PKCE or client credentials), secure storage and monitoring.
Read more
Static RBAC is unsafe for agentic cloud systems — AI enforces per-request, context-aware access with short-lived capability tokens.
Read more
Implement least-privilege IAM for CI/CD pipelines using OIDC, permission boundaries, CloudTrail and IAM Access Analyzer.
Read more
API gateways are the frontline for enforcing rate limits and throttling to protect backends and ensure fair traffic.
Read more
How RBAC protects API gateways: define roles, enforce via IAM, integrate with JWT/OAuth, monitor logs and audit access.
Read more