Terraform IAM Secrets: Best Practices
Zero secrets in state: use ephemeral resources, secret managers, encryption and least-privilege IAM to prevent credential leaks in Terraform.
Read more
Zero secrets in state: use ephemeral resources, secret managers, encryption and least-privilege IAM to prevent credential leaks in Terraform.
Read more
Practical guide to integrating E2E tests into CI/CD: plan workflows, prepare Docker/headless browser infrastructure, choose tools, parallelise tests and troubleshoot flakiness.
Read more
How DevOps integrate encryption, automate key rotation, enforce TLS and use tokenisation to meet PCI DSS 4.0.1 without slowing CI/CD.
Read more
Standardise tagging, account design, FinOps and governance across AWS, Azure and GCP to improve visibility and cut multi-cloud spend.
Read more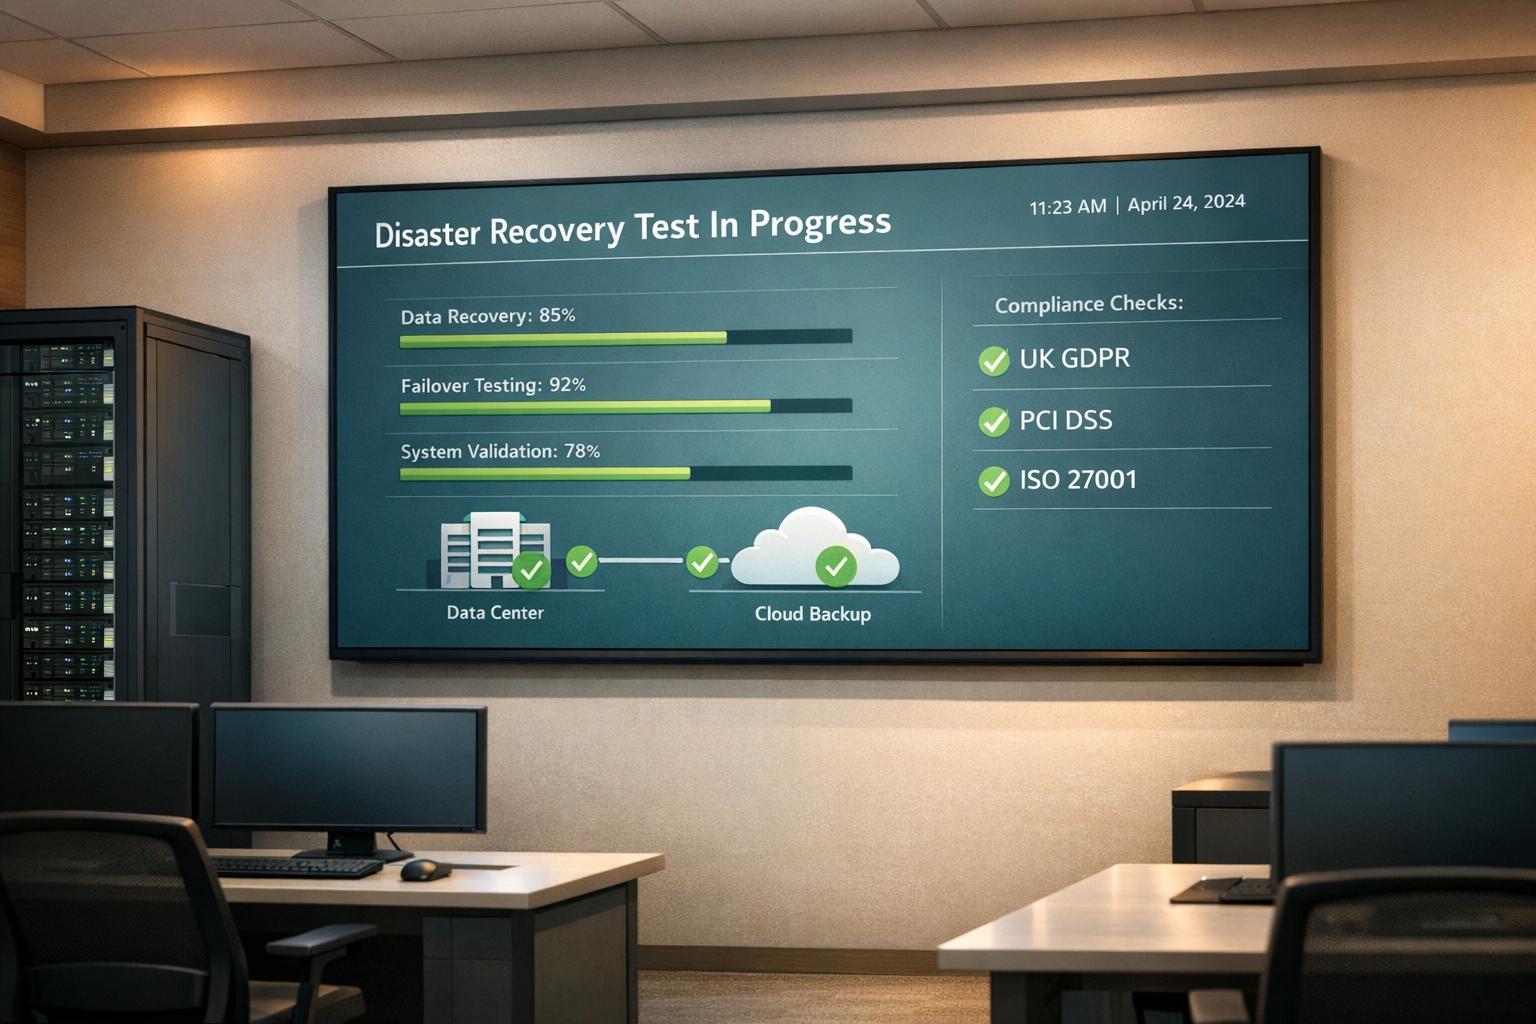
Regular hybrid cloud DR testing proves recoverability, enforces UK GDPR/PCI/ISO compliance, and exposes configuration gaps before they cause outages.
Read more
Checklist to build encryption policies for UK GDPR: AES-256, TLS 1.3, key management, retention, secure deletion, audits and access control.
Read more
Reduce cloud costs with Cluster Autoscaler: set accurate resource requests, tune scale-up/down, optimise node groups, prefer cheaper capacity, and monitor logs.
Read more
AI improves CDN performance for e‑commerce with predictive caching, smart routing and edge personalisation—cutting latency, raising cache hits, lowering costs.
Read more
Automate ISO 27001 compliance in private clouds with continuous monitoring, policy-as-code, drift control and automated evidence to speed audits and cut errors.
Read more
Practical steps to break DevOps silos: improve communication, set shared KPIs, form cross-functional teams, promote continuous learning and leadership support.
Read more
Integrate IaC into CI/CD pipelines: validate and test, security-scan, manage remote state, and plan/apply for repeatable, auditable deployments.
Read more
Integrate Policy as Code, automated SAST/SCA/IaC scans and continuous monitoring into CI/CD to keep deployments audit-ready and tamper-proof without slowing delivery.
Read more