ConfigMap Changes and Rolling Updates
Why ConfigMap edits don't restart Pods, how mounts and env vars behave, and when to use restarts, checksums, or reloaders.
Read more
Why ConfigMap edits don't restart Pods, how mounts and env vars behave, and when to use restarts, checksums, or reloaders.
Read more
Configure rolling updates, probes and cluster headroom so autoscaling can schedule surge Pods and keep Kubernetes rollouts zero‑downtime.
Read more
Use native cloud billing first; add open-source tools only to fill gaps for multi‑cloud, Kubernetes, governance or reporting.
Read more
Block most pipeline risk before release: shift security checks left, only block high-risk issues, and retain signed artefact evidence.
Read more
Compare seven Kubernetes rightsizing tools by control model, automation and cost impact to pick a safe, practical fit for your team.
Read more
Measure end-to-end flow, model pipelines as DAGs, split runner pools and scale from queue signals to improve CI/CD throughput.
Read more
Checklist-driven guide to designing durable stateful containers: storage, replication, StatefulSets, backups, RPO/RTO and tested failover.
Read more
Normalise and enrich alerts, enforce approval gates for risky containment, log every action and reduce MTTR safely.
Read more
Set RTO/RPO, replicate state, control writes and test DNS failover to keep serverless apps resilient across regions.
Read more
Compare seven cloud security monitoring tools by coverage, setup, alert quality, compliance and DevOps fit to pick the right tool.
Read more
Route AI agent tasks by risk with event-driven orchestration: stateful workflows, approval gates, retries and observability.
Read more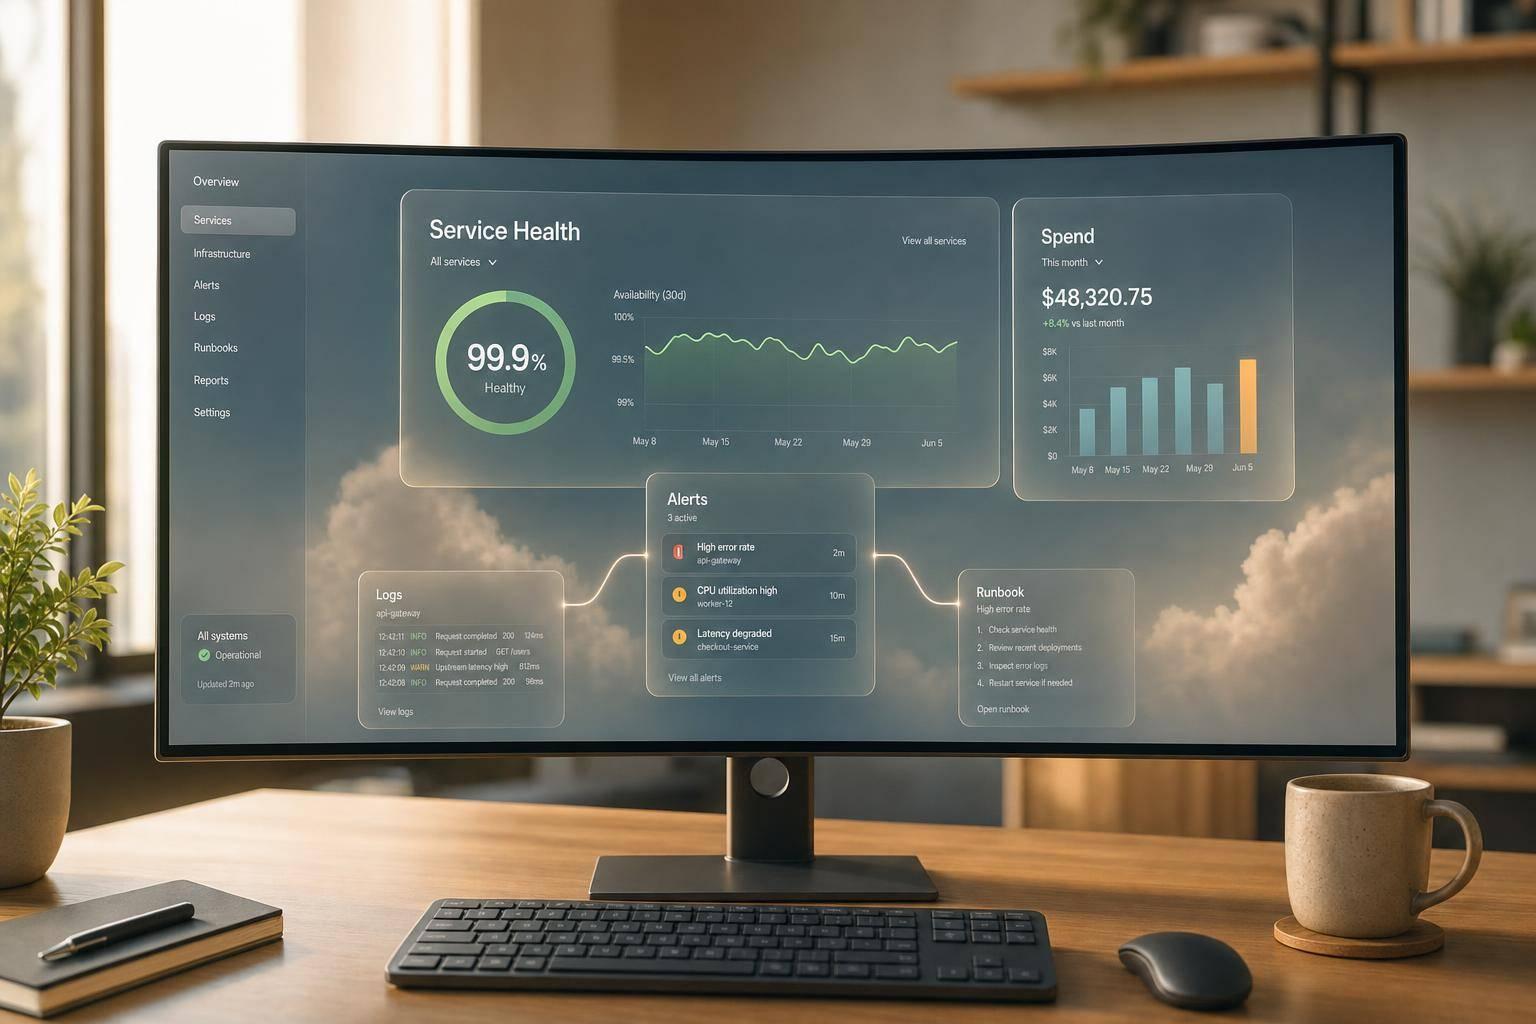
Design role-based cloud dashboards that prioritise service health and spend, link alerts to logs and runbooks, and reduce noise.
Read more