AI Model Extraction Tests: Rate Limits and Alerts
Test rate limits, detection and user impact to measure, tune and retest defences against distributed AI model extraction.
Read moreBlog posts in the Security Operations category
Test rate limits, detection and user impact to measure, tune and retest defences against distributed AI model extraction.
Read more
Explains spectral scoring to flag poisoned training samples, its limits, and why testing filter-and-retrain on your data is essential.
Read more
Deploy a read-only SharePoint connector for AI agents with access checks, minimal Graph permissions, cited retrieval and testing.
Read more
UK cloud team checklist for securing agentic AI: identity, least privilege, sandboxing, approvals and tamper‑evident logs.
Read more
Test prompt versioning tools against seven mandatory controls—immutable history, diffs, release labels, rollback, approvals, environment isolation and auditability.
Read more
Measure IaC drift by verified fixes, not alerts: ensure estate-wide coverage, timed scans, policy approvals and audit-ready closures.
Read more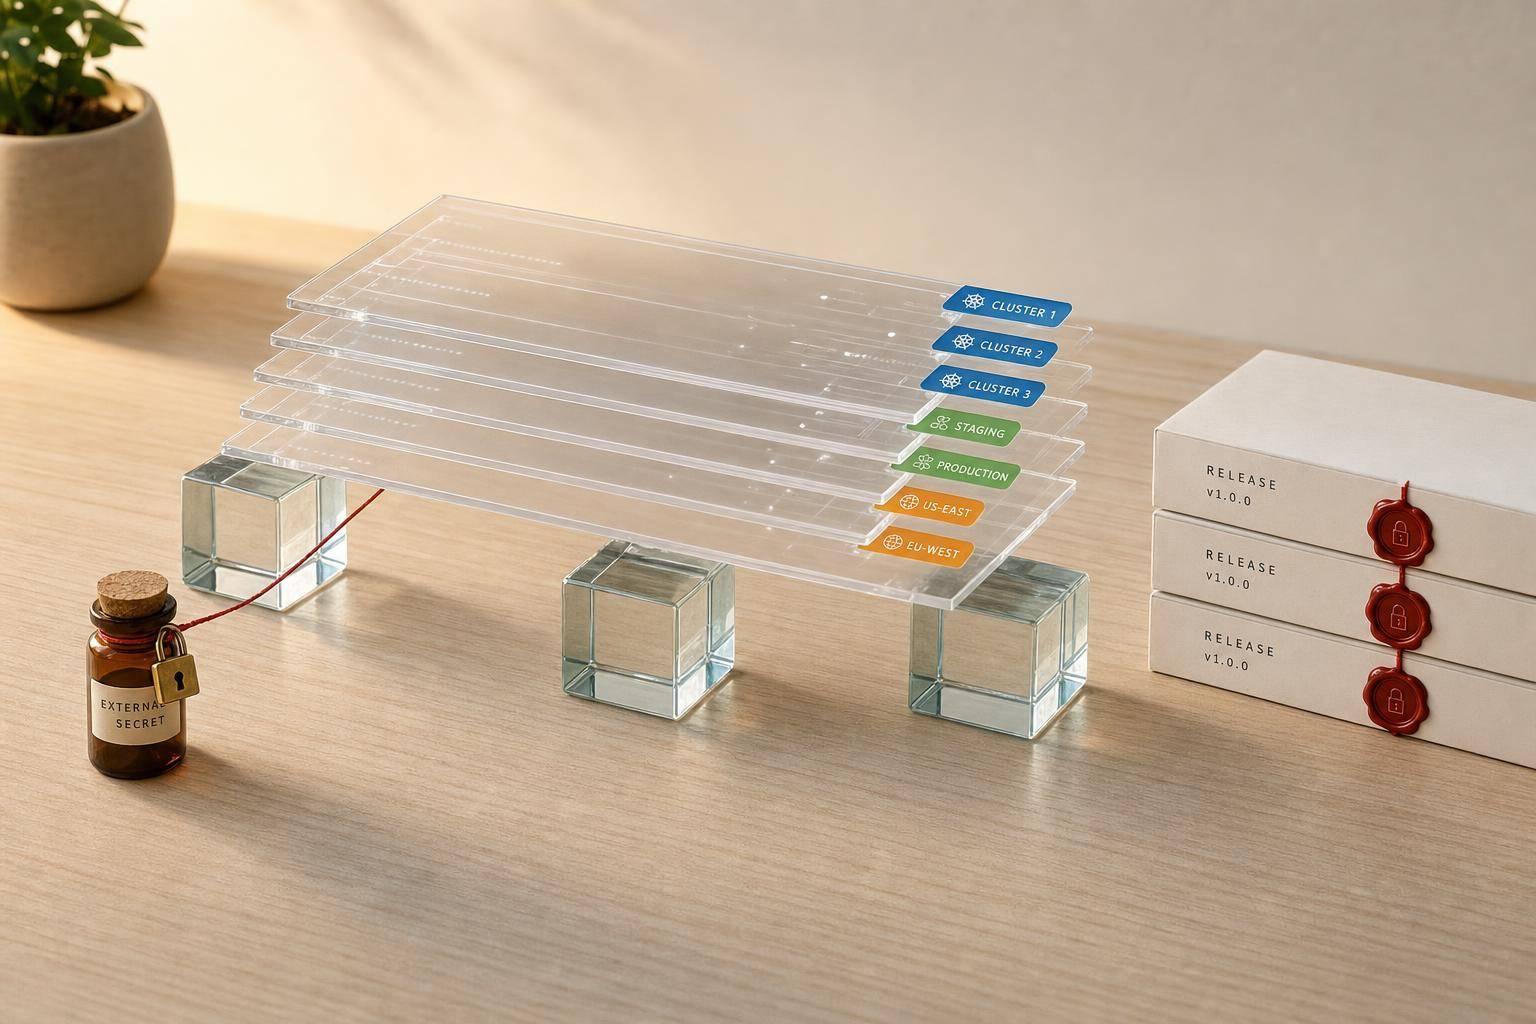
GitOps for multi-cluster Kubernetes: use bases/overlays, labels for targeting, external secret references, and promote immutable releases.
Read more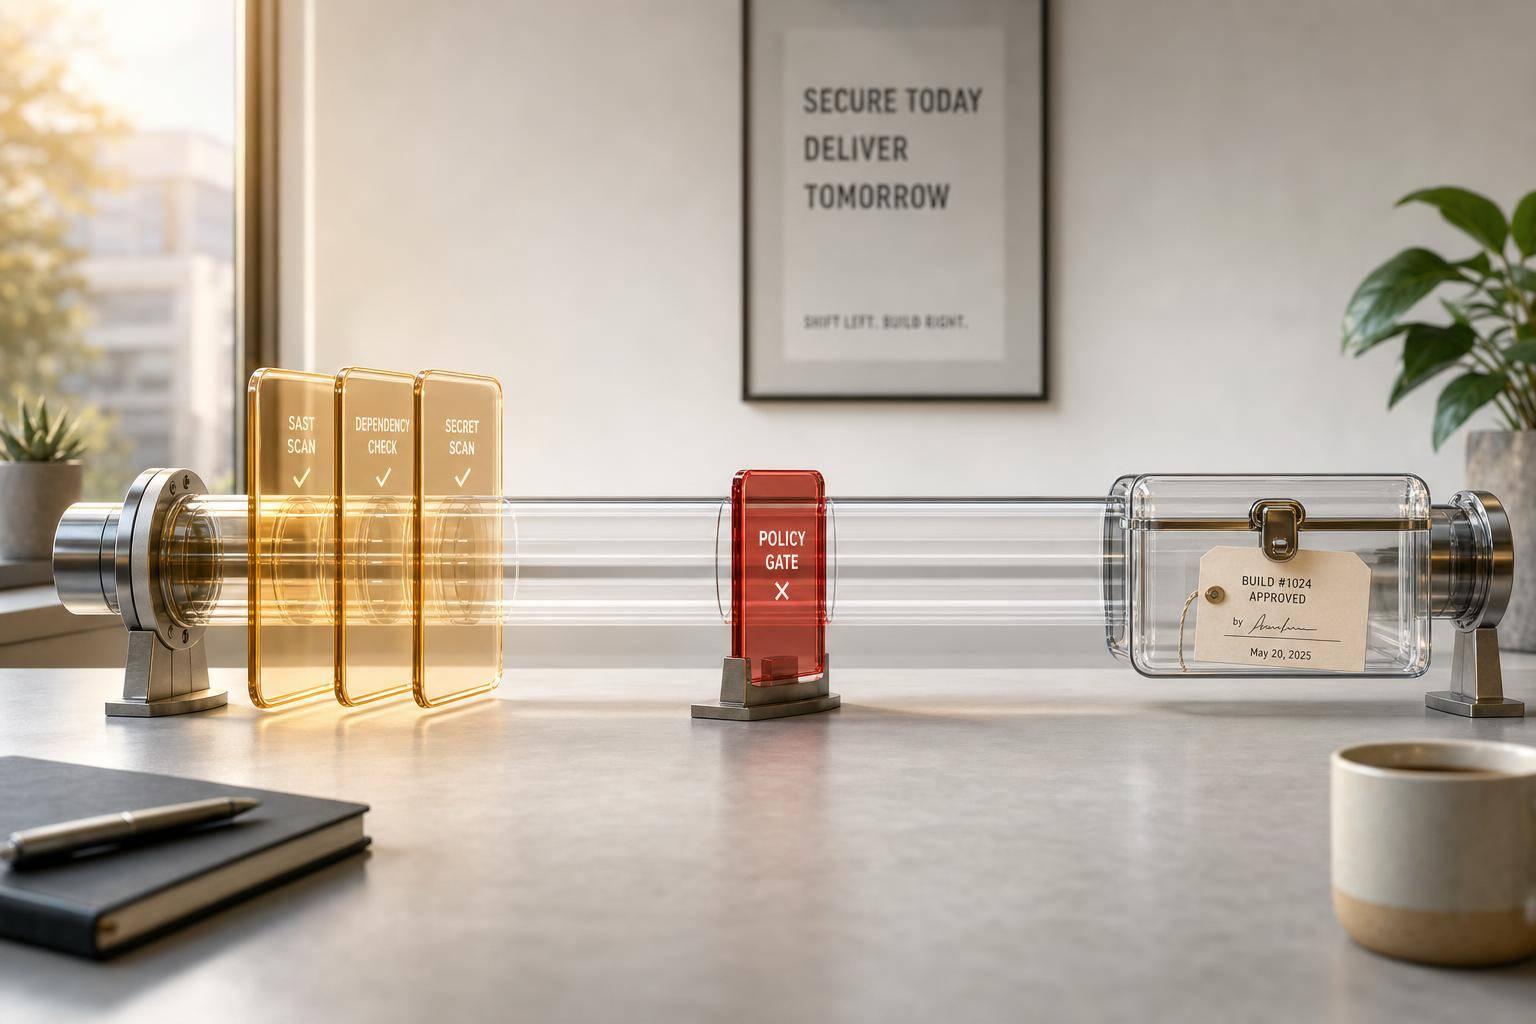
Block most pipeline risk before release: shift security checks left, only block high-risk issues, and retain signed artefact evidence.
Read more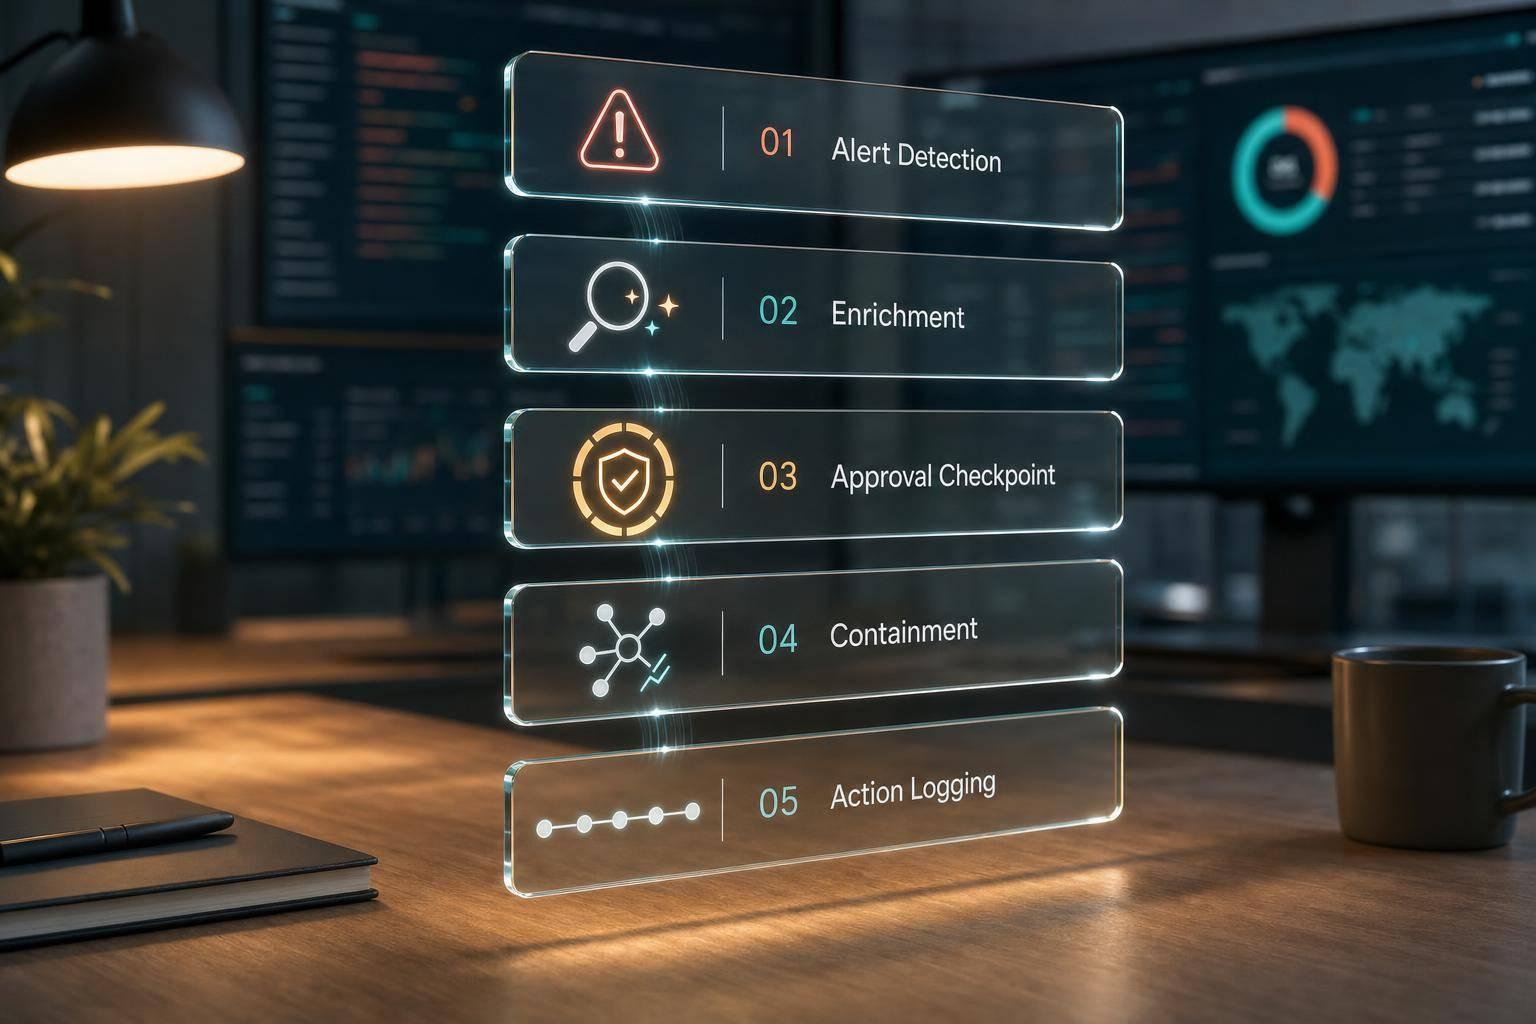
Normalise and enrich alerts, enforce approval gates for risky containment, log every action and reduce MTTR safely.
Read more